
Achieving ISO 27001 certification is a strategic milestone for organizations aiming to strengthen their information security posture. As data threats grow more sophisticated and regulatory expectations continue to rise, companies must demonstrate that they have a structured and reliable Information Security Management System (ISMS) in place. ISO 27001 provides the internationally recognized framework to achieve this, guiding businesses in identifying risks, implementing controls, and maintaining continual improvement in information security practices.
Despite its clear structure, implementing ISO 27001 can be challenging. Many organizations underestimate the depth of documentation required to meet certification standards. From defining the scope of the ISMS to conducting risk assessments and establishing policies, the documentation process can quickly become overwhelming. Without a structured starting point, teams may spend months drafting, reviewing, and revising documents—often leading to inconsistencies or gaps that delay certification audits.
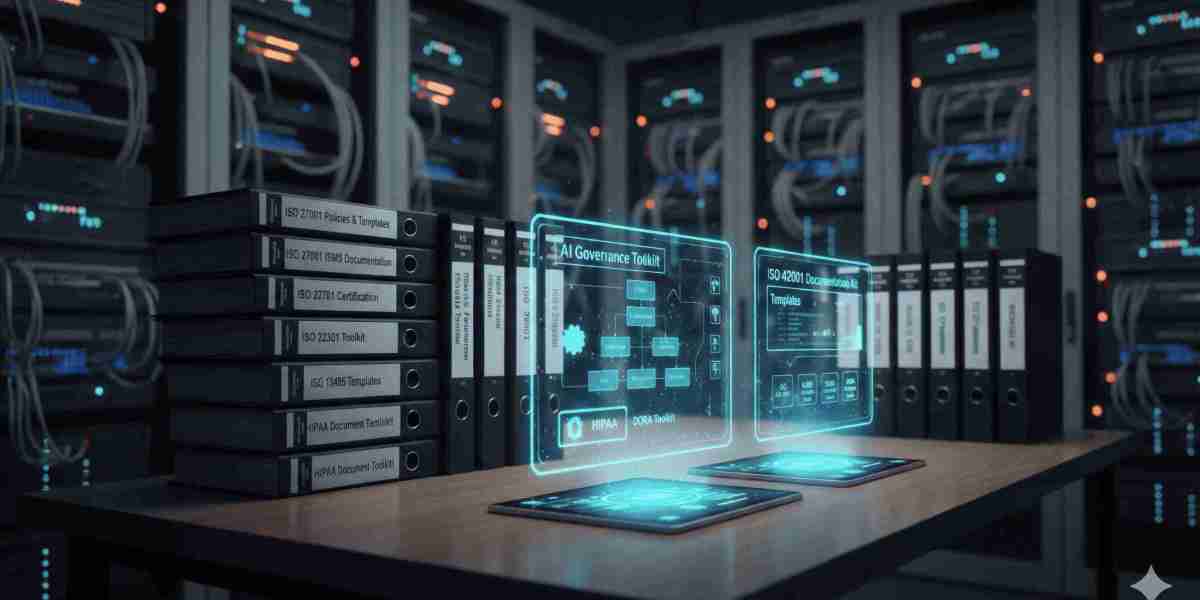
This is where professionally designed Iso 27001 Templates provide significant value. These templates offer a comprehensive framework covering essential policies, procedures, forms, and registers aligned with ISO 27001 requirements. Instead of creating documents from scratch, organizations can customize pre-built materials to reflect their operational context, industry requirements, and risk profile. This approach accelerates implementation, ensures alignment with the standard’s clauses and Annex A controls, and reduces the likelihood of missing critical compliance elements during audits.
Using structured templates also enhances internal efficiency. Clearly defined documents make it easier for employees to understand security responsibilities, follow established procedures, and contribute to a culture of information protection. Management gains better visibility into risk treatment plans, performance metrics, and corrective actions, while auditors can quickly assess compliance through well-organized records. In addition, standardized documentation simplifies ongoing maintenance of the ISMS, supporting regular updates, internal audits, and management reviews.
Ultimately, effective ISO 27001 implementation is not just about passing an audit—it is about building a resilient security framework that protects business continuity and stakeholder trust. Organizations that adopt structured documentation tools can focus more on strengthening controls and less on administrative burdens. With the right foundation in place, companies are better equipped to manage evolving threats, maintain regulatory alignment, and demonstrate their long-term commitment to safeguarding sensitive information.